






Everything posted by junkerderprovinz
-
Hey @castores Thanks, and not silly at all. The version you had only tried BombVault's own SSH key, never your password ("attempted methods [none publickey]"). 10.3.0 and later fix that. After updating, open the storage location, type the sub-account's password under Account password and press Add key. BombVault uses the password once to put its key on the Storage Box and doesn't keep it. Your server and user name are right. Just make sure SSH support is switched on for the sub-account in the Hetzner Console. If it still fails, post the new error here.
-
Hi @blaess, thanks for the report! Changing the region itself works. What you describe usually means garage.toml is no longer valid TOML after the edit, often because the quotes went missing: it has to be s3_region = "us-east-1". Garage can't start then, and the log shows "TOML decode error". With version 1.0.2 you don't need to edit the file. Update the container and enter us-east-1 in the new S3 Region field (if your template doesn't show it, add a variable S3_REGION). That also fixes the broken line. Your client has to use us-east-1 too. Cheers
-
TowerTorchYour server's UI on fire. Your disks stay cool. What is this?TowerTorch gives your whole Unraid server a fully revamped, modern interface, without replacing a single page. Dashboard, Main, Shares, Docker, Plugins, VMs and Settings get one clean, consistent look: tiles or lists, cards with switches instead of checkboxes, small animated pictures for the disks, the array and the mover, one accent colour or a rainbow, light and dark. Everything stays where Unraid put it, so nothing you know moves. Underneath, it looks after your containers: a start plan starts each one only once the container it depends on is actually ready, not just running, with per-container limits, a watchdog and schedules on top. A small Go daemon on a local unix socket does the work, and nothing leaves your server. Highlights & FeaturesDocker, Main, Shares, Plugins and VMs as lists or tiles; disk tiles only mention SMART, errors and rates when there is something to say Small pictures: the array's fill level as a vessel, platters that turn while a disk works, data flowing through SSDs, the mover and a parity check drawn while they run, all following your motion setting One accent colour or a rainbow, light and dark, shapes and motion levels, and a master switch that turns all theming off and keeps only the orchestration A start plan with dependency-ordered stages, so an app waits until its database is really ready; the plan window draws each chain lighting up in start order Readiness probes (running with grace, TCP port, HTTP, a log line or a command inside the container), each with its own failure policy A watchdog that restarts a crashed or unhealthy container, capped per hour, and schedules to start, stop or restart at fixed times per weekday Idle stop, inspired by ContainerNursery: a container that stays idle on CPU and network gets stopped; busy and host-network containers are skipped Live CPU, RAM and pinning limits through docker update without a restart, with P/E-core detection on Intel hybrid CPUs Upload and download caps per container, applied inside its own network namespace and read back live in the editor RequirementsUnraid 6.10+ Docker, and the VM manager if you want the VMs page Install from Apps, or under Plugins, Install Plugin with https://raw.githubusercontent.com/junkerderprovinz/towertorch/main/plugin/towertorch.plg Coming from CannonadeCommand? Install TowerTorch the same way. It takes over your settings, start plans and limits and removes the old plugin. Bugs, Problems, WishesSomething not working, a question or an idea? The best place for it is an issue on GitHub: github.com/junkerderprovinz/towertorch/issues. Everything stays in one place there, and nothing gets lost in a long thread. For a bug, open Settings → Utilities → TowerTorch → Info and press Bug report. TowerTorch saves a file with the versions, your settings and start plan and the end of the engine log, with passwords and other secrets taken out. Attach it, whether you post there or here, together with: The page and the action you were on (for example Docker → bandwidth gear → save) Browser and operating system A screenshot, if it is about how something looks CreditsBuilt in Go for Unraid. The idle stop is inspired by ContainerNursery. If TowerTorch lights up your Unraid, you can buy me a coffee. Self-hosted, AGPL-3.0 licensed: you run it, you own your server and the responsibility.
-
I don't know of a public sync status page. The closest thing is the app's page on ca.unraid.net (https://ca.unraid.net/apps/krusader-1gjxcb9125o7ip), which shows a Last Updated date and the template fields, including the language list. Right now it still shows the old template with Last Updated 2026-09-29, so CA hasn't picked up the new one yet. The change itself is already in the template file on GitHub: https://raw.githubusercontent.com/junkerderprovinz/unraid-apps/main/krusader/krusader.xml CA syncs on its own schedule and I can't speed it up. Until the new entries show up there, you can keep en_gb in the language field as you did.
-
@Revan335 You don't need separate mounts. The template maps the host path /mnt to /storage with the access mode Read/Write - Slave (rw,slave), so all of those show up as subfolders: /storage/user, /storage/cache, /storage/disks, /storage/remotes, /storage/disk1 and so on. Read/Write is needed for copying, moving, renaming or deleting. With read-only, Krusader can only browse. Slave matters for /mnt/disks and /mnt/remotes: Unassigned Devices mounts those after the container has started, and without slave the container keeps seeing an empty folder until it restarts. One warning that applies to any file manager on Unraid: don't copy or move between a user share path and a disk or cache path of the same share, for example from /storage/disk1/Movies to /storage/user/Movies. Both point at the same files, and that can truncate or delete them. Stay inside /storage/user, or inside the disk paths.
-
Hey @Revan335 Krusader handles this with a panel profile: 1. Open /storage in both panels, plus any tabs you want to keep. 2. Window → Profiles (Alt+Shift+L) → Add new entry, and give it a name, for example storage. 3. Settings → Configure Krusader → Startup, set Startup profile to the new entry, then OK. From then on Krusader opens with that profile on every start. The default, <Last session>, brings back the folders that were open when Krusader last closed, so if that's all you need, you can skip the profile.
-
Thanks for the kind words, and for tracking this down @FrequencyLost! Good catch: en maps to US English, and the US date format comes with it. The container already knew en_gb, the dropdown just didn't offer it. The template now has en_gb = English (UK), plus pt_br (Brazilian Portuguese) and zh_tw (Traditional Chinese), and the description says that the language also sets the date format. Community Applications should pick up the new template within a few hours. Your edited template keeps working as it is. The container only reads the code at the front, so your en_gb = UK English does the same thing as the new entry.
-
With KluthR's okay, a short note for anyone here who is looking at alternatives: I maintain BombVault, a backup and restore app in CA. It backs up containers together with their templates, VMs, the flash drive and ZFS datasets with restic, so the backups are deduplicated and encrypted, and it can copy them off-site. If you want to switch, BombVault can import your existing Appdata Backup archives as restore points, so your old backups come along. A container needs one BombVault backup first, so the restore knows its definition. Good to see chodeus working on the next update here, so Appdata Backup keeps going too. Pick whatever suits your setup. BombVault support thread: https://forums.unraid.net/topic/199509-support-junkerderprovinz-bombvault/
-
I maintain BombVault, a backup and restore app for Unraid in CA (containers, VMs, flash), so the built-in backup in Unraid 8 matters a lot to me. If someone from the team can share a few details: 1. What does it back up? Appdata, Docker templates and compose stacks, VMs, the flash drive, whole shares? 2. Is data encrypted before it leaves the server, and what engine runs underneath? 3. Will there be an API or hooks, so other tools can start a backup or read its status? Knowing this early would help me make BombVault fill the gaps rather than duplicate what ships with Unraid.
-
Hi @Mr.win7, thanks for trying it and for the detailed report! You found a real gap. StrawDroid rendered on the CPU by default, and passing /dev/dri alone didn't change that. v1.3.1 fixes it: EMULATOR_GPU now defaults to auto, so the emulator draws on whatever card you pass in. For your NVIDIA card: 1. Set EMULATOR_GPU to auto. An existing install keeps the old swiftshader_indirect value from its template. 2. Add --runtime=nvidia to Extra Parameters. 3. Set NVIDIA_VISIBLE_DEVICES to all. The updated template has a field for it; if yours doesn't, add it as a variable. This needs the Nvidia Driver plugin. Once it has started, the READY block at the end of the log has a Drawn: line, and it should name your card. If it says SwiftShader or llvmpipe instead, it's still on the CPU, and I'd like to see that log. About Redroid: it's faster because it isn't an emulator at all; Android runs straight on the host kernel. StrawDroid is built as a test rig that behaves like a phone (battery, sensors, Doze), so if you mostly want to use apps, Redroid may still suit you better. Keep in mind that Redroid only renders in software on NVIDIA cards. Thanks for offering to test, I'd love to hear how it runs on your card. For bug reports or feature requests, GitHub is the best spot, I see those fastest there: https://github.com/junkerderprovinz/strawdroid/issues
-
Hi @Moll, yes, that's what it means. Set up the way the guide describes, Config and Data sit on the SSD pool (/mnt/cache/appdata/opencloud/...), and uploads go straight to the array disk you set as Files. Nothing stops on the cache first and the mover isn't involved. Writing to the array is slower than the SSD, mostly because of parity, but with a few files you'll hardly notice. Since you only keep a few files, there's an even simpler option: leave Files empty. Then everything stays in Data on the SSD, and 256 GB goes a long way. Parity doesn't cover it there, so back up the appdata folder, for example with the Appdata Backup plugin. About /mnt/user: OpenCloud has no database and is constantly writing small files. During a big sync, Unraid's share layer can stop responding, and when it does, every container on /mnt/user hangs too until you reboot. With light use you might never run into it, but when it happens it takes the whole server down with it, so I can't recommend it. If a path still goes through the share layer, the container log warns you at every start. The bigger question for you is calendars, contacts and to-dos. OpenCloud doesn't do CalDAV/CardDAV itself. It passes those requests to a separate Radicale server and sits in front of it as a proxy (https://docs.opencloud.eu/docs/admin/configuration/radicale-integration). The template doesn't set that up, so out of the box you only get the file side. If calendars are the main reason you'd switch, keep Nextcloud for them for now or run Radicale on its own.
-
KnightLoaderDownloads everything, kneels to nothing. What is this?KnightLoader is a download manager for hosters, debrid services, torrents, Usenet, videos and streams. Hoster links go through the debrid service you already pay for, torrents to the built-in client or to a debrid service, .nzb files to your own Usenet servers, and videos and streams to yt-dlp. Whatever is left goes to a headless JDownloader that KnightLoader sets up by itself inside the container. The image brings yt-dlp, ffmpeg and the Java runtime along, so there is nothing to install beside it. The same program also runs as a desktop app for Windows, macOS and Linux, and an Android app and a browser extension send it links from wherever you are. Highlights & FeaturesLinks wait in the collector first. It checks each one and shows what will fetch it, and Packagizer rules sort them into packages and folders as they arrive Instances, the Android app and the browser extension find each other with twelve words, across networks, without an account, a domain or a port forward. The relay can be the project's, your own ParleyPort, or an instance that is reachable from outside Torrents through the built-in client or a debrid service, and Usenet from your own servers with par2 repair or through TorBox and Premiumize.me Sonarr and Radarr see it as qBittorrent or SABnzbd Links come in from Click'n'Load, the browser extension, the phone's share sheet, a watched folder, and DLC, CCF and RSDF container files When a download finishes, archives are unpacked without outside tools, checksums are checked, files land in folders built from templates, and a media library can be told to rescan Coming from JDownloader? KnightLoader takes over your accounts, rules, archive passwords and the open download list, with a preview first A password, two-factor authentication and passkeys under Settings, Security, and an app key that seals the secrets in the appdata folder 42 languages Images: junkerderprovinz/knightloader:latest on Docker Hub and ghcr.io/junkerderprovinz/knightloader:latest, for amd64 and arm64 RequirementsUnraid 6.10+ Keep the WebUI on your LAN until you set a password under Settings, Security: until then anyone who can reach the port can use it An app key is optional but worth it. Run openssl rand -hex 32 in a terminal and paste the result into the App key field (KL_APP_KEY). Keep it with your other passwords, because KnightLoader does not start on sealed data without the same key The template runs the container as nobody:users (--user 99:100) with UMASK 000, so the account you use over SMB can move, rename and delete what KnightLoader downloads Bugs, Problems, WishesSomething not working, a question or an idea? The best place for it is an issue on GitHub: github.com/junkerderprovinz/knightloader/issues. Everything stays in one place there, and nothing gets lost in a long thread. For a bug, whether you post it there or here, these help: Unraid version (Settings → System Information) Image tag (latest or a pinned version) The file from the Bug report button under Settings, Info: the build, the settings with every password removed and the latest log lines If the container does not start, the last lines of its log (Docker tab, KnightLoader icon, Logs) What kind of link it was (hoster, debrid, torrent, Usenet, video) and what you expected against what happened CreditsDownloads run on the engine of Gopeed, videos and streams on yt-dlp and ffmpeg, and JDownloader takes the hoster links nothing else claims. The RSDF and CCF readers follow JDownloader's GPL-3.0 container plugins. If KnightLoader has earned a place on your server, toss a coin to your knight: you can buy me a coffee. Self-hosted, AGPL-3.0 licensed: you run it, you own your data and the responsibility.
-
Hi @MisterSparkle, thank you for the detailed report, the log showed exactly what happens. This is a bug in BombVault and not in your setup: a timer that stops a backup after two hours without progress kept running during the off-site copy, which reports no progress to it. Every copy that needed more than two hours after a backup was cancelled, and the rclone errors in your log are only that cancellation. Version 9.9.3 fixes it. 1. Unraid web UI, Docker tab: click Check for Updates at the bottom, then apply update in the BombVault row. 2. In BombVault open Settings, Off-site and click Replicate now in the Containers section. The copy runs in the background. 3. The first copy to your SFTP server can take many hours. The Dashboard shows that it is running, and "Off-site replication failed" should not come back. Replicate now was never affected, so step 2 already works on your current version if you want to start right away. If nothing arrives on the SFTP server after the update, please open an issue on GitHub and paste the new log: Docker tab, click the BombVault icon, Logs, select everything with Ctrl+A, copy with Ctrl+C, and paste it into the issue between two lines of three backticks. https://github.com/junkerderprovinz/bombvault/issues
-
Hi @PsiKoTicK, thank you for reporting this. You found a real gap: BombVault had no way back in after a lost password. Version 9.9.2 is out now and adds one, so pick whichever of these two ways suits you. Option 1: update, then reset on the login page 1. Unraid web UI, Docker tab: click Check for Updates at the bottom, then apply update in the BombVault row. 2. Open BombVault and click Forgot password? on the login page. 3. Back on the Docker tab, click the BombVault icon and choose Logs. Near the end there is a yellow line: PASSWORD RESET CODE: XXXX-XXXX 4. Enter that code and a new password on the login page. You are signed in right away. A code is valid for 10 minutes. Option 2: without updating 1. Docker tab: click the BombVault icon and choose Stop. 2. Open the Unraid terminal (the >_ icon at the top right of the web UI), paste this line and press Enter: sqlite3 /mnt/user/appdata/bombvault/bombvault.sqlite "UPDATE settings SET auth_password_hash='', totp_enabled=0, totp_secret='', totp_recovery='';" 3. Docker tab: click the BombVault icon and choose Start. BombVault opens without a login, and you set a new password under Settings, Security. The line prints nothing when it worked. If you changed the "Config" path in the template, put your own path in front of /bombvault.sqlite. I tested both ways on Unraid 7.3.2. For bug reports and feature requests GitHub is the best place, I see them fastest there: https://github.com/junkerderprovinz/bombvault/issues
-
@J1mB0b Great to hear it works now, and thanks for sticking with it! - On the phone, the OpenCloud Android app can already do this: tap the ⋮ next to a document, pick "Open in Euro-Office (web)", and the editor opens in your phone's browser. - .ocnote is OpenCloud's own note format. Only OpenCloud's built-in editor reads it, so notes stay in the OpenCloud web UI for now. - For .odt, .ods and .odp, Collabora Office is free on Android and iOS and opens all three. If you run into a bug or have a feature wish, GitHub is the best place, I see those fastest there: https://github.com/junkerderprovinz/opencloud/issues
-
SeafileOne container. No homework. What is this?Seafile is a file sync and share server with desktop and mobile clients, libraries you can encrypt on the client, and built-in wikis. Its official image expects MariaDB, Redis and the notification server as containers of their own on a shared network, plus a JWT key you make by hand. This is the official Seafile 14 image with a small startup step in front of it, so it installs from one template: the secrets are generated on the first start, and MariaDB, Redis and the notification server can run inside the same container when you have none of your own. Seafile's own scripts still set it up, start it and upgrade it. Highlights & FeaturesThe JWT key, the database password and, if you leave it empty, the admin password are generated on the first start and kept in secrets.env in the data folder; the log names a generated admin password Built-in MariaDB and Redis, each switched on in the template and listening only inside the container; external servers stay the default The notification server, switched on in the template, so the desktop and mobile clients see changes when they happen A missing hostname, database host or Redis host stops the start with one line saying what to set, instead of a "Page unavailable" Seafile stops before the built-in database on shutdown The data folder keeps the official layout, so a setup from another Seafile template switches over by pointing at the same folder Images: junkerderprovinz/seafile:latest on Docker Hub and ghcr.io/junkerderprovinz/seafile:latest, for amd64 RequirementsUnraid 6.10+ A MariaDB and a Redis server, or Built-in MariaDB and Built-in Redis set to true Server hostname set to the address your clients use, such as 192.168.1.10:8000 or seafile.example.com; desktop clients cannot sync when it is wrong Seafile 14 is still labelled testing upstream and cannot be downgraded: back up the data folder and the database before every update Bugs, Problems, WishesSomething not working, a question or an idea? The best place for it is an issue on GitHub: github.com/junkerderprovinz/seafile/issues. Everything stays in one place there, and nothing gets lost in a long thread. For a bug, whether you post it there or here, these help: Unraid version (Settings → System Information) Image tag (latest or a pinned version) Output of docker logs --tail 200 Seafile Whether you use the built-in MariaDB and Redis or your own, and whether Seafile runs behind a reverse proxy Whether this is a new install or one you switched over from another Seafile template CreditsAll the real work is Seafile (AGPL-3.0) by Seafile Ltd., with MariaDB and Redis next to it. This project only makes their official image install from one template. If it spared you an evening of compose files, you can buy me a coffee. Independent packaging, not affiliated with Seafile Ltd. AGPL-3.0 licensed: you run it, you own your data and the responsibility.
-
Hi @J1mB0b, thanks a lot for the kind words, and for the donation! That helps keeping up the work! No worries about the thread, Euro Office questions are fine here. You didn't do anything wrong. Euro Office on its own only shows its start page. The editor shows up inside OpenCloud once the two are connected, and your post made me simplify exactly that part. Please update both containers first (Docker tab, "Check for Updates", then "apply update"), so you're on OpenCloud 1.4.0 and Euro Office 1.2.0. Then: 1. In the Euro Office template, set a JWT secret if you haven't yet (any long random text) and click Apply. 2. In the OpenCloud template, set Web office suite to euro-office, Office document server URL to the address the Euro Office WebUI button opens (for example http://192.168.1.10:9900), and Office WOPI secret to the same text as the JWT secret. Click Apply. 3. Open OpenCloud and reload the page. The New button now offers Document, Spreadsheet and Presentation, and Word or Excel files open in the editor when you click them. If the entries aren't there right away, wait a minute and reload again. You don't need the admin panel or the example page, and you don't have to change anything about JavaScript. That message comes from the example page and you can ignore it. After the update, the Euro Office WebUI button opens a start page that shows whether the editor is ready and which address to enter in OpenCloud. For Tailscale later: OpenCloud passes the editor through its own address, so only OpenCloud has to be reachable from outside.
-
Hi @reinv, thanks for the kind words and for the detailed request! ShipLog 3.5.0 is out and can read a changelog file. Open the ShipLog status page (http://<your-server>:8484), click source in the Domoticz row and paste the file's URL. The GitHub file view link works too, ShipLog turns it into the raw link itself: https://github.com/domoticz/domoticz/blob/development/History.txt The bubble then shows the top section of the file. For Domoticz that's "Version 2026.4", the upcoming release that collects all the beta changes. The beta builds (2026-beta.18377 and so on) never show up as headings in History.txt, so ShipLog can't pick the exact span there. For projects with a CHANGELOG.md and version headings it shows the sections between your running and the newest version. For bug reports or feature requests, GitHub is the best spot, I see those fastest there: https://github.com/junkerderprovinz/shiplog/issues
-
ArrowLoopTwo-way file sync that shows you the plan before it moves anything. What is this?ArrowLoop keeps two folders in step: an Unraid share and a laptop, a share and a cloud, or two servers. It remembers what both sides last agreed on, so it can tell a file that is new on one side from one that was deleted on the other. Before a run it lists every change with its direction and its reason; untick what you disagree with, and nothing is touched until you start it. It reaches every rclone backend, compiled in rather than shelled out to: local folders and shares, SMB, SFTP, S3-compatible storage, WebDAV clouds such as Nextcloud and OpenCloud, and the rest. The same engine runs as this container, as a desktop app for Windows, macOS and Linux, and as an Android app. Highlights & FeaturesEvery change is listed before a run, and single ones can be dropped Deletions go to a trash on the side that loses the file, never straight away A run that would delete more than half the known files stops and says so, and a side that suddenly lists nothing is refused, because an unmounted disk looks exactly like an emptied folder An edit on both sides keeps both versions, and an edit beats a deletion Schedules, real-time watching, scripts before and after a run, and a notification when a run fails Encryption at the destination through rclone's crypt A password, two-factor authentication and passkeys for the WebUI, under Settings, Security 42 languages, light and dark themes Images: junkerderprovinz/arrowloop:latest on Docker Hub and ghcr.io/junkerderprovinz/arrowloop:latest, for amd64 and arm64 RequirementsUnraid 6.10+ Keep the WebUI on your LAN until you set a password under Settings, Security: until then anyone who can reach it can start a sync that deletes files The Data path is mounted read-write, because a two-way job writes to both sides Bugs, Problems, WishesSomething not working, a question or an idea? The best place for it is an issue on GitHub: github.com/junkerderprovinz/arrowloop/issues. Everything stays in one place there, and nothing gets lost in a long thread. For a bug, whether you post it there or here, these help: Unraid version (Settings → System Information) Image tag (latest or a pinned version) Output of docker logs --tail 200 ArrowLoop The job's two sides (a local path, an SMB share, a cloud and so on), and what you expected against what happened Whether the run stopped with a message, and its text CreditsBuilt on rclone, embedded as a library, which is what lets one engine reach every backend. If ArrowLoop keeps your files where they belong, you can buy me a coffee. Self-hosted, AGPL-3.0 licensed: you run it, you own your data and the responsibility.
-
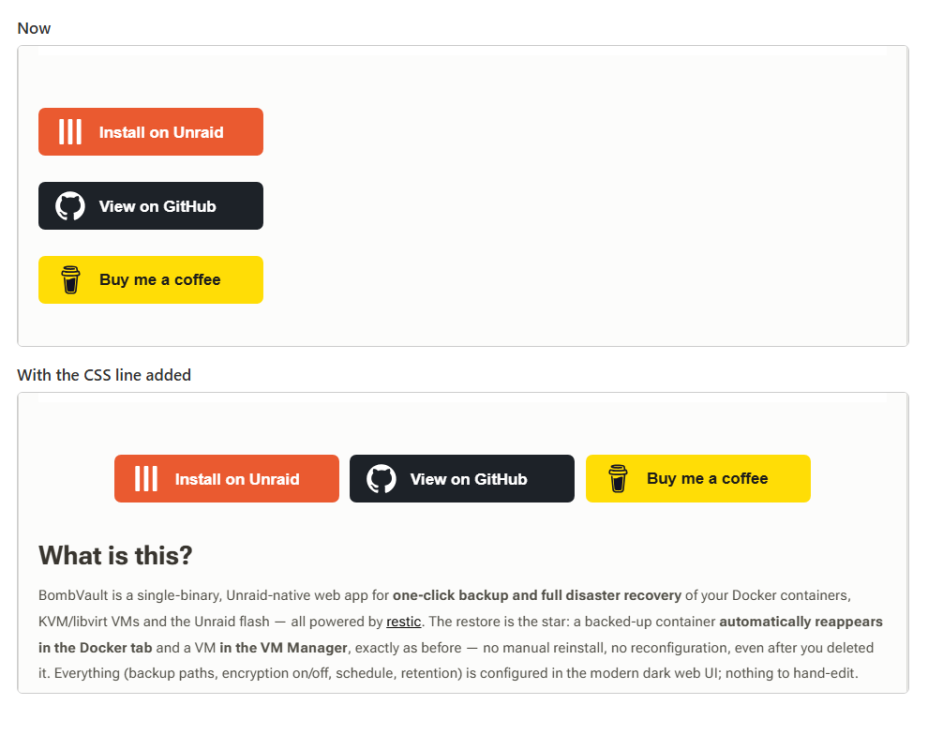
Hi @elibosley, My support threads have a row of three link buttons under the banner: three images in one centered paragraph. They used to sit side by side in the middle. Now each one sits on its own line, flush left. You can see it in my BombVault support thread: https://forums.unraid.net/topic/199509-support-junkerderprovinz-bombvault/ Every image in a post gets the class ipsRichText__align--block, which is display: block, so the paragraph's text-align: center doesn't reach them anymore. The image menu only offers Normal, Left and Right, so I can't fix it from inside the post, and tables have no alignment at all. The theme already has .ipsRichText__align--inline { display: inline-block }, but the editor doesn't let you pick it. Either "inline" could go into the image alignment menu, or this one line of custom CSS would do it: .ipsRichText p[style*="text-align:center"] .ipsRichText__align--block:not(.ipsRichText__align--width-fullwidth) { display: inline-block; } I tried the line in the browser on the live thread. The three buttons go back into one centered row, and full-width images like the banner stay as they are. Before and after screenshot attached. Thanks!
-
Hey @dam_j, glad it's working now, and thanks for letting me know! About the iOS app: your guess is right. The App Store version has its look built in and doesn't pull the branding from your server, so the Branding app only changes the web interface and the sign-in page. To get your own logo and colours into the app, you'd have to build your own copy from OpenCloud's source code, which has a branding file for exactly that. That needs an Apple developer account and your own distribution through the App Store or TestFlight, so it's well outside what the container can do. Nextcloud's apps do pick up the server colours, but OpenCloud's apps don't read any theming from the server at all. For bug reports or feature requests, GitHub is the best spot, I see those fastest there: https://github.com/junkerderprovinz/opencloud/issues
-
Hi @dam_j, no, it's not the language. An update only pulls the new image. Unraid never adds new fields to the edit page of a container that's already installed, so "Branding admin app" won't show up on its own, however many updates you install. I've reported that to Unraid: https://github.com/unraid/webgui/issues/2765 You need to add the variable once by hand: 1. In the Unraid web interface, open the Docker tab. 2. Click the OpenCloud icon and choose Edit. 3. Scroll to the bottom and click "Add another Path, Port, Variable, Label or Device". 4. In the window that opens, set Config Type to Variable, Name to Branding admin app, Key to BRANDING_APP and Value to true, then click Save. 5. Click Apply at the bottom of the edit page. Unraid recreates the container with the new variable. After that, sign in to OpenCloud with an admin account. Branding is in the app menu next to your avatar. If it still isn't there, please open an issue on GitHub with the container log. I see those fastest there: 1. On the Docker tab, click the OpenCloud icon and choose Logs. A window with the log opens. 2. Click into that window, press Ctrl+A to select everything, then Ctrl+C to copy it. 3. Open https://github.com/junkerderprovinz/opencloud/issues and click "New issue". 4. Describe what you see, then paste the log between two lines that contain only three backticks (```) so it stays readable. Thanks!
-
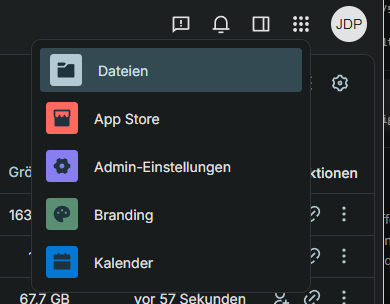
Branding is new in the template, and Unraid doesn't add new template fields to a container that's already installed, so your edit page doesn't show it yet. You can add it by hand: 1. On the Docker tab, click the OpenCloud icon and choose Edit. 2. At the bottom, click "Add another Path, Port, Variable, Label or Device". 3. Set Config Type to Variable, Name to Branding admin app, Key to BRANDING_APP and Value to true. Save, then Apply. After the restart, sign in with an admin account and open the app menu next to your avatar. Branding shows up there; other accounts don't see it.
-
@dam_j Small update on this: v1.3.0 ships a Branding app in the web interface, so the logo and the text no longer need a hand-edited theme.json. Set Branding admin app to true in the advanced view of the template and restart once. Admins then get a Branding entry in the app menu for the instance name and slogan, a logo for light and dark mode, the favicon, the login background, and whether the sign-in card is light, dark or follows the browser. The login page shows all of it as well, and saved changes apply without another restart. Colours are not in the app. While it is on, it rewrites the theme list in themes/_branding/theme.json at every start, so custom colours in that file get replaced. If the palette matters more to you than the app, leave the toggle off and keep editing the file by hand. It is off by default, so nothing changes if you do nothing.
-
Hey @dam_j Glad it works! Yes, you can, but not from a settings page. OpenCloud reads a theme file from the Data folder: Open https://YOUR-SERVER-IP:9200/themes/opencloud/theme.json (or your own OpenCloud URL) and save it. That's the theme currently in use. Put it at /mnt/user/appdata/opencloud/data/web/assets/themes/opencloud/theme.json (create the folders) and your logo in an assets folder next to it. Edit it: text: common.name and common.slogan logo: common.logo and clients.web.defaults.logo, e.g. themes/opencloud/assets/mylogo.svg colours: clients.web.themes[].designTokens.roles (primary is the main one) Hard-refresh the browser (Ctrl+F5). The login page uses the logo from the same file. For a background image there, add the variable IDP_LOGIN_BACKGROUND_URL to the template with the URL of your image. The login page's own colours are built in and don't follow the theme.




